
Law 21,663 ceased to be a regulatory promise and became the real roadmap that today governs cybersecurity in Chile, and no one explains it better than those who apply it on a daily basis.
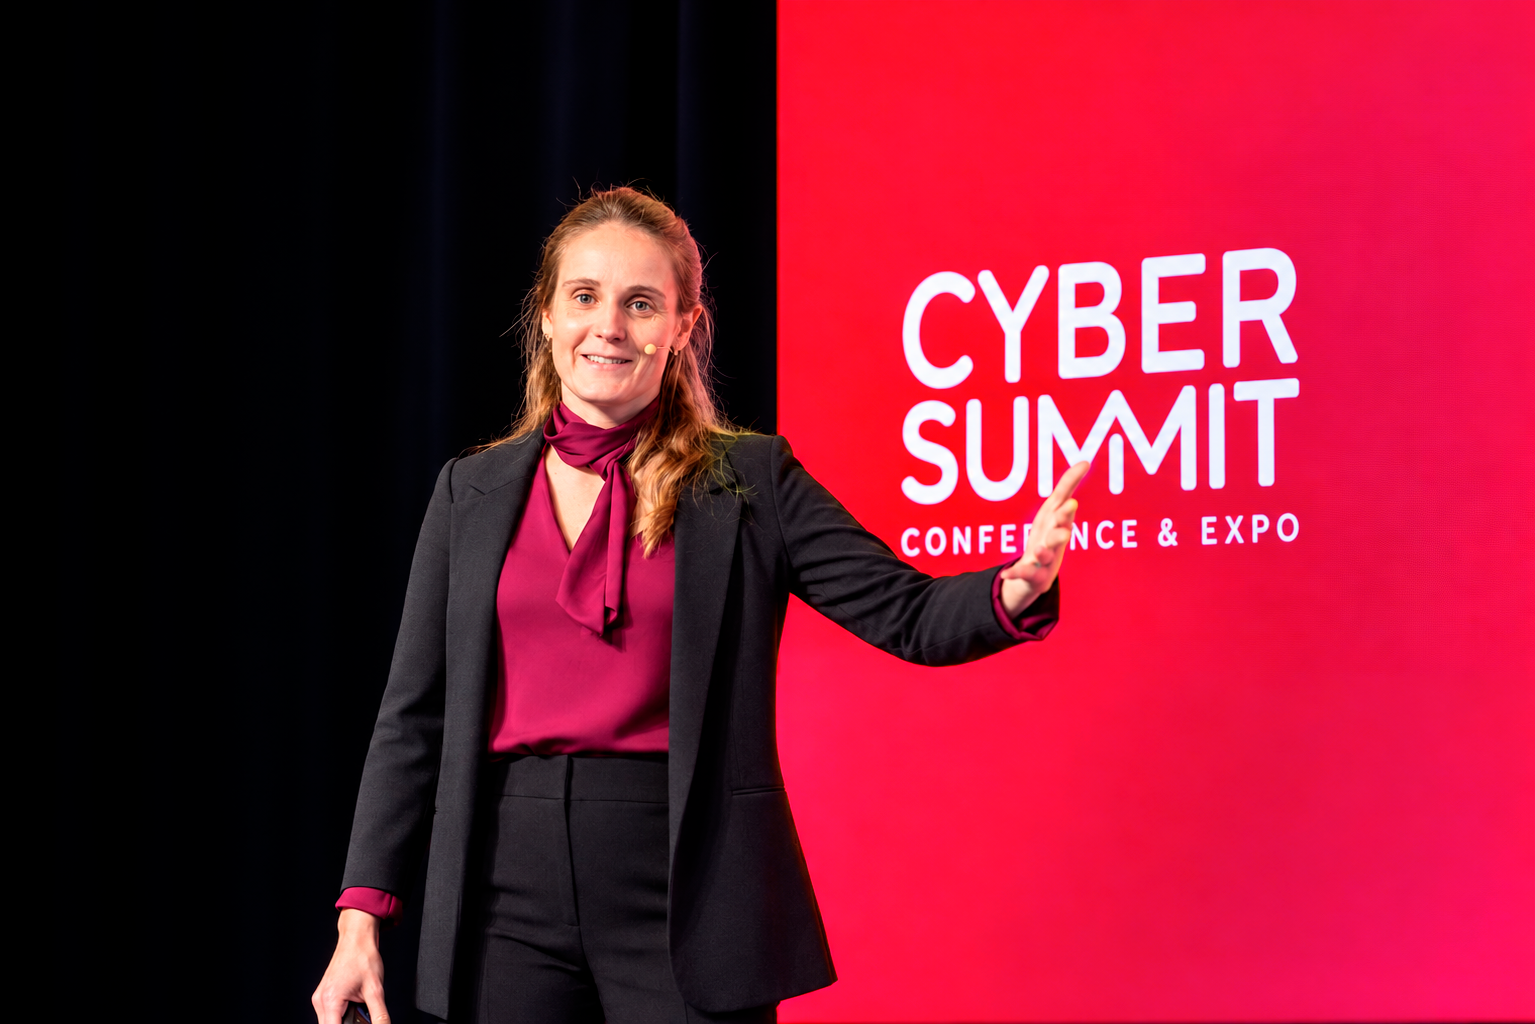
Michelle Bordachar Benoit, National Director (s) of the National Cybersecurity Agency (ANCI), opened the Industrial Cyber Summit Chile 2026 with a direct and unadulterated overview of this new regulatory landscape: what the law requires, who has to report, and what comes next.
Bordachar started with the why. If Chile wants to consolidate itself as a medium power —that is, to weigh in on international decisions without the size of the country being a limiting factor—, it needs a cybersecure and more resilient ecosystem. That idea is not just rhetoric: the international relations the agency is building give Chile access to strategic information and technical capabilities that it would otherwise not have, and they put it on the table where global cybersecurity rules are decided. A country absent from that table, he warned, risks leaving its autonomy at risk from cyberspace.
What the ANCI does (and what it doesn’t)
The agency's role, summarized by its own director, has three legs: preventing, containing, and managing cybersecurity incidents; promoting the development of culture and capabilities within the country; and providing a secure interconnection network for state agencies. To fulfill that role, the ANCI has regulatory, fiscal, and sanctioning powers over both the public and private sectors.
One of the points that Bordachar insisted on clarifying, because it continues to generate confusion, is who is required to report. It is not just the Operators of Vital Importance (OIV): any public or private institution that provides services within any of the regulated sectors is an essential service and, therefore, an obligated entity, regardless of its size. A two-person company that provides digital services in a regulated sector has the same reporting obligation as a company with thousands of employees.
What needs to be reported, and how soon
The law has not yet issued specific mandatory standards for all sectors: the agency’s first year was focused on establishing itself, from renting offices to setting up the incident reporting platform. To advance in regulations, the ANCI must conduct public consultations before setting standards, and it already did so this year. Meanwhile, what already exists is the general cybersecurity duty and, above all, the duty to report any incident with significant impact.
Bordachar was frank about the broadness of these concepts: «interrupt» and «affect» are weak verbs, and «integrity» is such a broad concept that practically any system with personal data falls within it. Her recommendation, in the event of doubt, is to report: if the agency determines that it was not a significant incident, they simply report it and the institution continues on its way; if it was, ANCI helps manage it with guidelines and recommendations, although it may not always send people to the scene.
The deadlines, on the other hand, are specific and it’s worth having them on hand.
| Time limit | What needs to be delivered |
|---|---|
| 3 hours from the time it is known | The observable effects of the incident |
| 72 hours later | Update of the initial assessment and indicators of commitment |
| 15 days from when the incident stops being ongoing | Final report |
Source: Michelle Bordachar Benoit (ANCI), opening keynote at the Industrial Cyber Summit Chile 2026.
The taxonomy that defined these deadlines was deliberately designed to be simple, something that at the time earned it criticism from experts for being «not very sophisticated.» It was a deliberate decision: it has to be able to report on the same level as a large institution with dedicated security teams as well as a small business without any cybersecurity experts.
Reports like radar: the Rutifay case
The value of this system, Bordachar explained, lies in the fact that the reports feed into threat research and proactive warnings before vulnerabilities are exploited. The Rutifay case is the most concrete example: when the leak came to light, the ANCI had already been monitoring dark web chats and was able to determine that much of the information being sold corresponded to previous vulnerabilities, some even dating back to the cybersecurity framework itself, recombined in a more attractive way for sale. That joint investigation with the affected institutions contributed to the arrest of one of the involved individuals.
The agency is equally strict on the other side: it systematically refuses to hand over, in the face of requests for transparency, which institutions reported or suffered incidents. For Bordachar, that confidentiality is the basis of the trust that underpins the entire system; the day that that information is revealed, the regulated parties stop reporting honestly.
This same logic of aggregated data led to another concrete result: by analyzing five cybersecurity incidents in state agencies, the agency detected a pattern of behavior from an attacker group and was able to issue secret instructions to vulnerable institutions. Thanks to this, at least 21 institutions avoided becoming victims of the same ransomware, with an estimated savings of more than 1 billion pesos for the public sector, counting only direct costs for specialized support.
Why the ANCI does not require ISO 27001
One of the questions that the agency receives most often is why it does not directly impose a standard like ISO 27001. Bordachar’s answer ties into the same principle of simple taxonomy: the ANCI regulates enormously diverse institutions, from microenterprises to corporate giants, spread across 15 different sectors, and requiring such a sophisticated standard would leave out a large portion of them from compliance. There is also an uncomfortable fact behind that decision: the majority of the serious incidents and cyberattacks that the agency has seen occurred in institutions that were indeed ISO 27001 certified. They performed very well on paper, but in practice people were not complying.
From there they emerged the «Nine basic things», Published on the agency’s website: nine measures that, according to their own data, could prevent 80% of incidents and cyberattacks. Bordachar was clear that imposing them is not enough: you have to explain to the teams why each one is necessary. The double authentication factor, for example, is not «just another annoying step,» but the most effective way to prevent the compromise of accounts, which in 2025 was the main cause of incidents in Chile, followed by exploiting vulnerabilities and operational causes. Today, the list repeats itself with a variant that worries more and more: phishing, increasingly sophisticated, no longer appeals to the typical «prince who promises an inheritance» but to real data from the victim —travels, miles, passport number— stolen from airlines and other platforms, to offer credible promotions.
What's coming: a citizen report and «Puerto Seguro»
Bordachar concluded with a first: in the coming days the agency will launch a citizen reporting portal, distinct from the incident reporting portal that already exists. It will include two programs. One is a «bug bounty» program for state institutions and private companies that want to join. The other is «Puerto Seguro,» protected by Article 19 of the law, which obliges the agency to maintain strict secrecy about what it receives through ethical hacking. Thanks to this measure, the ANCI has already been able to alert institutions about vulnerabilities before they were discovered and exploited by criminals.
The underlying message, with which Bordachar closed his presentation, was to return to the basics: normative sophistication is useless if the nine basic measures are not understood and not applied every day. That is, today, the real map of the Cybersecurity in critical infrastructures in Chile: a young agency, still in its infancy, that is already using its data to prevent attacks before they happen, while it is finishing building the regulatory framework that will be required tomorrow. Those who want to delve into how this connects to the Convergence of IT and OT in the Chilean energy sector or with the rest of the scientific agenda of the event they can review the Panel on quantum computing and AI from the same Cyber Summit Chile 2026.
